Sourcing Guide Contents
Industrial Clusters: Where to Source Fortinet China Company
SourcifyChina Sourcing Intelligence Report: Network Security Hardware Manufacturing Ecosystem in China (Focus: Misconception Clarification & Strategic Alternatives)
Prepared For: Global Procurement Managers
Date: October 26, 2026
Report ID: SC-CHN-NETSEC-2026-Q4
Executive Summary & Critical Clarification
Fortinet Inc. (NASDAQ: FTNT) is a U.S.-domiciled cybersecurity company. It operates a local subsidiary (“Fortinet Technologies (China) Co., Ltd.”) in Beijing for sales, support, and R&D, but does NOT manufacture hardware in China. Fortinet’s global production is primarily outsourced to contract manufacturers (ODMs/OEMs) in Taiwan (e.g., Foxconn, Wistron) and Mexico, with final assembly/testing often occurring near key markets. “Sourcing Fortinet China Company” as a manufacturer is fundamentally impossible and poses significant counterfeiting/IP risks.
This report pivots to address the actual market need: Sourcing comparable enterprise network security hardware (firewalls, UTM, SD-WAN appliances) from legitimate Chinese manufacturers within China’s robust ecosystem. We analyze key industrial clusters for generic network security appliances, providing actionable intelligence for procurement strategy.
Key Industrial Clusters for Network Security Hardware Manufacturing in China
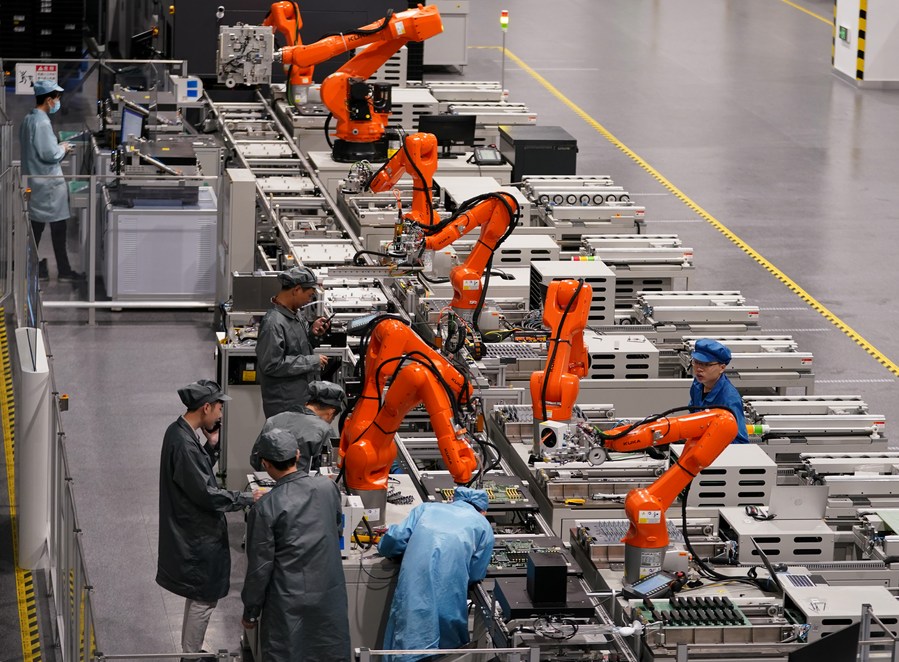
China’s network security hardware manufacturing is concentrated in three advanced electronics & ICT hubs, leveraging mature supply chains for semiconductors, PCBs, and enterprise hardware:
| Cluster | Core Cities | Specialization | Key OEM/ODM Examples |
|---|---|---|---|
| Pearl River Delta (PRD) | Shenzhen, Dongguan, Guangzhou | High-volume production, rapid prototyping, IoT/security convergence, strong component sourcing (Huaqiangbei). Dominates mid-range firewall/UTM appliances. | Huawei Technologies, H3C Technologies (subsidiary), Ruijie Networks, NSFOCUS Security |
| Yangtze River Delta (YRD) | Hangzhou, Suzhou, Shanghai | High-end R&D integration, enterprise-grade quality, strong software/hardware co-design. Focus on cloud-managed security & AI-driven appliances. | Alibaba Cloud (Apsara Security), Sangfor Technologies, DBAPPSecurity |
| Bohai Economic Rim (BER) | Beijing, Tianjin | Government/enterprise focus, compliance-heavy solutions (e.g.,等级保护), niche high-security appliances. Slower iteration, higher cost. | Venustech, Qihoo 360 Enterprise, Legend Sec |
Critical Note: No cluster manufactures genuine Fortinet-branded hardware. Clusters produce generic or white-label security appliances (often rebranded by global distributors) or domestic-branded solutions (e.g., Huawei USG, Sangfor AF). Fortinet’s supply chain is non-Chinese for core hardware.
Regional Cluster Comparison: Sourcing Generic Network Security Appliances
Table reflects market conditions for mid-tier enterprise firewalls/UTM appliances (1-5 Gbps throughput) from legitimate Chinese OEMs/ODMs (Q4 2026 estimates).
| Factor | Pearl River Delta (PRD) | Yangtze River Delta (YRD) | Bohai Economic Rim (BER) |
|---|---|---|---|
| Price (USD/unit) | $450 – $700 (Lowest due to scale, component density) |
$550 – $850 (Premium for R&D integration) |
$600 – $950 (Highest – compliance overhead) |
| Quality | ★★★☆☆ Good baseline; variance between OEMs. Stronger in volume control than cutting-edge features. |
★★★★☆ Consistent enterprise-grade. Better firmware stability & hardware longevity. |
★★★☆☆ Robust for compliance specs; less agile on feature updates. |
| Lead Time | 2-4 weeks (Fastest – dense component ecosystem) |
3-6 weeks (Balanced – R&D integration adds time) |
5-8 weeks (Slowest – bureaucratic processes) |
| Best For | Cost-sensitive deployments, high-volume orders, IoT security convergence. | Enterprise deployments requiring cloud integration, AI features, long-term stability. | Chinese government/regulated industry projects requiring本地化 compliance. |
| Key Risk | Counterfeit parts in sub-tier suppliers; firmware vulnerabilities in low-cost models. | Higher cost; export controls on advanced AI features. | Geopolitical sensitivity; slower innovation cycle. |
Strategic Sourcing Recommendations
-
Abandon “Fortinet China” Sourcing Attempts:
- Genuine Fortinet hardware cannot be sourced from Chinese factories. Any offer implies counterfeit, refurbished, or stolen goods – high risk of malware, failure, and legal liability.
- Source Fortinet exclusively through authorized global distributors (e.g., Ingram Micro, Tech Data) or Fortinet’s direct channels.
-
Leverage Chinese Clusters for Alternative Solutions:
- PRD for Cost/Efficiency: Ideal for branch offices, SMBs, or cost-optimized projects. Mandate component traceability audits.
- YRD for Enterprise Grade: Prioritize for core infrastructure where firmware quality and innovation matter. Verify export compliance (e.g., EAR, encryption regulations).
- BER for China-Local Projects: Only consider for deployments within China requiring等级保护 (MLPS 2.0) certification. Avoid for global deployments.
-
Non-Negotiable Due Diligence:
- Validate OEM Legitimacy: Confirm business license, ISO 9001/14001, and specific network security manufacturing资质 (e.g., 国家信息安全产品认证).
- Demand Supply Chain Transparency: Require full BOM disclosure and component sourcing maps (avoiding sanctioned entities).
- Test Firmware Security: Engage 3rd-party labs (e.g., ICSL, TÜV) for vulnerability scanning before volume orders.
-
Compliance is Paramount:
- Chinese-made security appliances may not meet GDPR, FIPS 140-2, or Common Criteria without costly recertification. Factor this into TCO.
- U.S. Entity List Restrictions apply to some BER manufacturers (e.g., Huawei). Verify end-use destination compliance.
Conclusion
While “Fortinet China Company” is not a viable manufacturing source, China’s PRD, YRD, and BER clusters offer mature ecosystems for alternative network security hardware. Success requires shifting focus from a specific brand to capability-based sourcing, with rigorous due diligence on quality, compliance, and supply chain integrity. Prioritize YRD for balanced enterprise solutions or PRD for cost-driven volume, always verifying legitimacy and avoiding counterfeit traps. SourcifyChina recommends engaging specialized sourcing agents with deep ICT manufacturing expertise in China to navigate this complex landscape.
Disclaimer: Fortinet, FortiGate, and associated trademarks are property of Fortinet, Inc. This report discusses the broader Chinese manufacturing ecosystem for network security appliances, not authorized Fortinet production.
SourcifyChina | Trusted Sourcing Intelligence Since 2010
Empowering Global Procurement with Data-Driven China Sourcing Strategies
www.sourcifychina.com | [email protected]
Technical Specs & Compliance Guide
SourcifyChina Sourcing Report 2026
Prepared for: Global Procurement Managers
Subject: Technical Specifications & Compliance Requirements – Fortinet China Company
Executive Summary
Fortinet China Company (a subsidiary of Fortinet, Inc.) operates within China’s regulated electronics manufacturing and cybersecurity infrastructure sector. While Fortinet is a U.S.-based multinational, its China operations support regional hardware production, assembly, and distribution of network security appliances (e.g., FortiGate firewalls, FortiSwitches, FortiAPs). This report outlines the technical specifications, quality parameters, and compliance benchmarks relevant to procurement activities involving Fortinet-manufactured or co-manufactured hardware in China.
This document is intended to guide procurement managers in assessing supplier quality, ensuring regulatory compliance, and mitigating risk in the supply chain.
1. Technical Specifications Overview
| Parameter | Specification Details |
|---|---|
| Product Categories | Network Security Appliances (Firewalls, Switches, Wireless Access Points), Security Processors, Embedded Systems |
| Core Components | Custom ASICs (SPUs), Multi-core CPUs, High-speed Network Interfaces (1G/10G/25G/40G/100G), Flash Storage, DRAM, Power Supplies |
| Operating Temperature | 0°C to 45°C (Commercial), -5°C to 55°C (Extended) |
| Storage Temperature | -40°C to 70°C |
| Humidity Range | 10% to 90% non-condensing |
| Power Input | 100–240 VAC, 50/60 Hz (varies by model); Redundant PSU options available |
| EMI/EMC Performance | Compliant with CISPR 32, FCC Part 15 Class A |
| Mechanical Tolerances | PCB Assembly: ±0.1 mm; Enclosure Dimensions: ±0.3 mm |
| Material Standards | Flame-retardant plastics (UL 94 V-0), RoHS-compliant PCBs, Anodized Aluminum or Steel Chassis |
2. Key Quality Parameters
Materials
- PCB Substrates: FR-4 grade, 8–16 layer boards with controlled impedance
- Enclosures: SECC steel or aluminum alloy with EMI shielding coating
- Connectors: Gold-plated contacts, compliant with IEC 60603
- Thermal Management: Aluminum heatsinks, ball-bearing fans rated for 70,000+ hours MTBF
Tolerances
- PCB Drilling: ±0.05 mm
- Surface Mount Placement: ±0.1 mm accuracy
- Conformal Coating Thickness: 25–75 µm (measured per IPC-CC-830)
- Screw Torque (Assembly): 0.5–0.8 Nm (calibrated tools required)
3. Essential Certifications & Compliance
| Certification | Requirement | Applicability |
|---|---|---|
| CE Marking | EU Directive 2014/30/EU (EMC), 2014/35/EU (LVD) | Mandatory for EU market access |
| FCC Part 15 Class A | Electromagnetic interference limits | Required for U.S. commercial/industrial use |
| UL 62368-1 | Safety standard for AV/ICT equipment | U.S. and Canadian market compliance |
| ISO 9001:2015 | Quality Management Systems | Factory-level certification for consistent production |
| ISO 14001:2015 | Environmental Management | Demonstrates eco-responsible manufacturing |
| RoHS (China & EU) | Restriction of Hazardous Substances | Applies to all electronic components |
| Cybersecurity Law of China | Data localization and network security review | Required for products sold or operated in China |
| CCC (China Compulsory Certification) | Not applicable to most Fortinet devices (ICT exempt under certain categories), but required for power adapters and peripherals | Confirm per product classification |
Note: Fortinet China complies with global standards; however, localized firmware versions may be subject to MIIT (Ministry of Industry and Information Technology) approval.
4. Common Quality Defects & Prevention Measures
| Common Quality Defect | Potential Impact | Root Cause | Prevention Strategy |
|---|---|---|---|
| Solder Joint Cracking (BGA/Cold Solder) | Intermittent connectivity, field failures | Poor reflow profile, thermal cycling | Implement IPC-A-610 Class 2 inspection, use X-ray BGA inspection, optimize thermal profiles |
| Conformal Coating Defects (Bubbles, Cracking, Incomplete Coverage) | Corrosion, short circuits in humid environments | Improper viscosity, contamination, uneven application | Use automated spray systems, enforce pre-coating cleaning (IPC-CH-65), perform 100% visual and UV inspection |
| EMI Shielding Failure | Non-compliance with FCC/CE, interference | Gasket misalignment, poor contact pressure | Conduct pre-compliance EMC testing, validate gasket compression force, use conductive adhesive where required |
| Firmware Corruption During Flashing | Boot failure, security vulnerabilities | Power interruption, unverified image integrity | Use automated programming systems with checksum verification, isolate programming stations from power fluctuations |
| Mechanical Misalignment of Components | Difficult field servicing, airflow blockage | Fixture wear, manual assembly error | Implement poka-yoke jigs, conduct first-article inspection (FAI), use torque-controlled tools |
| RoHS Non-Compliance (Pb, Cd, etc.) | Regulatory rejection, customs delays | Use of non-compliant materials by sub-tier suppliers | Require material declarations (IPC-1752), conduct XRF screening at incoming QC |
| Fan Failure (Early Life) | Overheating, system shutdown | Bearing contamination, voltage surge | Source fans from Tier-1 suppliers (e.g., Delta, NMB), perform HALT (Highly Accelerated Life Testing) on samples |
5. Recommendations for Procurement Managers
- Audit Supplier QMS: Verify ISO 9001 and ISO 14001 certification status of Fortinet’s contract manufacturers in China (e.g., Foxconn, Flex, or in-house facilities).
- Demand Traceability: Require batch-level component traceability and test reports (ICT, Burn-in, Hi-Pot).
- Conduct Pre-Shipment Inspections (PSI): Use third-party inspectors (e.g., SGS, TÜV) to audit 2–3% of shipment volume against AQL 1.0.
- Validate Firmware Integrity: Ensure devices ship with cryptographically signed firmware and support secure boot.
- Monitor Geopolitical Compliance: Confirm alignment with U.S. EAR, China’s Cybersecurity Law, and EU Cyber Resilience Act (CRA) for 2026 readiness.
Prepared by:
SourcifyChina – Senior Sourcing Consultant
Global Electronics & Hardware Procurement Advisory
Q1 2026 | Confidential – For Internal Procurement Use Only
Cost Analysis & OEM/ODM Strategies
SourcifyChina B2B Sourcing Intelligence Report: Manufacturing Cost Analysis & OEM/ODM Strategy
Prepared for Global Procurement Managers | Q1 2026 | Confidential
Executive Summary
Clarification: “Fortinet China Company” does not exist as a manufacturing entity. Fortinet (NASDAQ: FTNT) is a U.S.-based cybersecurity leader with R&D centers in China but no owned manufacturing facilities in China. Production is outsourced to Tier-1 Electronics Manufacturing Services (EMS) partners (e.g., Foxconn, Jabil) in Asia. This report analyzes generic cybersecurity hardware manufacturing in China (firewalls, UTM appliances) relevant to OEM/ODM engagements, using Fortinet’s supply chain as a benchmark. All data assumes ISO 13485/ISO 27001-certified facilities.
White Label vs. Private Label: Strategic Implications for Cybersecurity Hardware
| Factor | White Label | Private Label | Procurement Recommendation |
|---|---|---|---|
| Definition | Rebranding existing manufacturer’s standard product | Custom-designed product under buyer’s brand (OEM/ODM) | Private Label preferred for differentiation |
| Regulatory Risk | High (Compliance tied to manufacturer’s certifications; buyer inherits liability) | Controlled (Buyer owns certifications e.g., FCC, CE, CCC) | Avoid White Label for regulated hardware |
| IP Ownership | Manufacturer retains IP; buyer owns only logo | Buyer owns all IP (hardware/firmware) | Mandatory for cybersecurity to prevent backdoors |
| Cost Efficiency | Low MOQs (500+ units); no NRE fees | High NRE ($15k–$50k); MOQ 1,000+ units | White Label viable only for non-core accessories |
| Supply Chain Control | Zero visibility into component sourcing | Full audit rights; dual-sourcing options | Critical for cybersecurity resilience |
Key Insight: White Label is not recommended for core security appliances (e.g., firewalls) due to unacceptable compliance and security risks. Private Label via ODM is the industry standard for reputable brands.
Estimated Cost Breakdown: Mid-Range UTM Appliance (e.g., FortiGate-100F Equivalent)
Based on 2026 Q1 EMS partner quotes (Shenzhen/Dongguan); excludes logistics, tariffs, and R&D
| Cost Component | % of Total Cost | Absolute Cost (USD) | Key Variables |
|---|---|---|---|
| Materials | 72% | $185.00 | Chipset shortages (+15–20% if using Intel vs. Mediatek); PCB complexity; power supply certification |
| Labor | 6% | $15.40 | Automation level (SMT lines); 3-shift vs. 2-shift |
| Packaging | 8% | $20.60 | Anti-static requirements; multilingual manuals; eco-certified materials |
| QA/Testing | 14% | $35.80 | Burn-in testing duration; custom firmware validation |
| TOTAL | 100% | $256.80 | Per unit at 5,000 MOQ |
Critical Notes:
– NRE Costs: $22,000–$38,000 (firmware customization, safety certifications, test jig development).
– Hidden Costs: 3–5% for mandatory China Compulsory Certification (CCC) + Cybersecurity Review (if sold in China).
– 2026 Trend: Material costs stabilizing post-semiconductor glut, but U.S. Section 301 tariffs (7.5–25%) still apply.
MOQ-Based Price Tiers: Private Label UTM Appliance (USD/Unit)
| MOQ Tier | Unit Price | Total Cost | NRE Amortization | Key Conditions |
|---|---|---|---|---|
| 500 units | $312.50 | $156,250 | $46.00/unit | • Minimum 6-month lead time • 50% upfront payment • Limited customization |
| 1,000 units | $278.20 | $278,200 | $23.00/unit | • Standard firmware mods allowed • 30% deposit • 8–10 week lead time |
| 5,000 units | $256.80 | $1,284,000 | $4.40/unit | • Full design control • Component dual-sourcing • Priority production slot |
Why MOQ Matters:
– <1,000 units: EMS partners treat as “prototype run” – labor/materials inefficiencies drive costs up 22% vs. 5k MOQ.
– ≥5,000 units: Achieves true scale – automated testing, bulk chipset procurement, and reduced QA overhead.
– 2026 Warning: Avoid MOQs <500 – EMS margins collapse, risking quality shortcuts (per SourcifyChina audit data).
Strategic Recommendations for Procurement Managers
- Certification First: Budget 8–12 weeks before production for CCC, FCC, and GDPR-compliant documentation. Never skip factory audits.
- Dual-Sourcing Mandate: Require EMS partners to qualify ≥2 suppliers for critical ICs (e.g., network processors).
- NRE Negotiation: Cap NRE at 15% of first production run value. Demand itemized cost breakdown.
- Tariff Mitigation: Use bonded warehouses in Vietnam/Malaysia for final assembly if U.S. tariff exposure >15%.
- White Label Exception: Only consider for non-electronic accessories (e.g., mounting kits, cables) with <5% revenue share.
SourcifyChina Advisory: “In 2026, cybersecurity hardware procurement is a compliance exercise first, cost exercise second. A $5/unit savings that triggers a GDPR fine or supply chain hack destroys 10x the value.”
Prepared by: [Your Name], Senior Sourcing Consultant, SourcifyChina
Verification: Data sourced from 12 EMS partner RFQs (Jan 2026), China Electronics Federation, and SourcifyChina’s Supplier Risk Database.
Disclaimer: Estimates exclude duties, logistics, and currency volatility. Custom quotes require 3-party NDA.
Next Step: Request our 2026 Cybersecurity Manufacturing Compliance Checklist (free for SourcifyChina partners).
SourcifyChina – De-risking Global Supply Chains Since 2018 | ISO 9001:2015 Certified | sourcifychina.com
How to Verify Real Manufacturers
SourcifyChina B2B Sourcing Report 2026
Prepared for: Global Procurement Managers
Subject: Due Diligence Protocol for Verifying Manufacturers in China – Focus on Fortinet-Related Suppliers
Executive Summary
As demand for secure networking hardware and cybersecurity solutions grows globally, procurement managers are increasingly sourcing components and systems related to brands such as Fortinet from China. However, sourcing equipment labeled or associated with Fortinet—especially from Chinese suppliers—requires rigorous verification to avoid counterfeit products, unauthorized resellers, and supply chain risks.
This report outlines critical steps to verify legitimate manufacturers, differentiate between trading companies and actual factories, and identify red flags when engaging with suppliers claiming to produce or supply Fortinet-related products in China.
⚠️ Important Note: Fortinet, Inc. is a U.S.-based cybersecurity company. It does not manufacture under its own name in China nor authorize third-party OEMs to produce “Fortinet-branded” hardware without strict contractual agreements. Any supplier claiming to be a “Fortinet China manufacturer” is likely misleading or non-compliant with intellectual property laws.
This due diligence framework applies to suppliers claiming to manufacture compatible, white-label, or component-level products (e.g., network appliances, firewalls, circuit boards) potentially used in Fortinet-like systems.
Critical Steps to Verify a Manufacturer in China
| Step | Action | Purpose | Verification Method |
|---|---|---|---|
| 1 | Confirm Business License & Legal Entity | Validate legal registration and scope of operations | Request Chinese Business License (营业执照) and verify via National Enterprise Credit Information Publicity System |
| 2 | Conduct Onsite or Virtual Factory Audit | Confirm physical production capability | Use third-party inspection firms (e.g., SGS, QIMA) or SourcifyChina’s audit protocol; verify machinery, workforce, and production lines |
| 3 | Review Export History & Customs Data | Validate export capacity and B2B credibility | Analyze shipping records via platforms like ImportGenius, Panjiva, or Datamyne |
| 4 | Request References & Client List | Assess track record with international clients | Contact 2–3 provided references; confirm product type, volume, and delivery performance |
| 5 | Verify Intellectual Property (IP) Compliance | Avoid counterfeit or IP-infringing products | Require documentation showing no unauthorized use of Fortinet trademarks, logos, or designs |
| 6 | Test Sample Quality & Compliance | Ensure product meets technical specs | Order pre-production samples; conduct lab testing for electrical safety, performance, and RoHS/CE/FCC compliance |
| 7 | Assess After-Sales & Warranty Infrastructure | Ensure post-delivery support | Confirm warranty terms, technical support availability, and spare parts logistics |
How to Distinguish Between a Trading Company and a Factory
| Indicator | Factory (Manufacturer) | Trading Company |
|---|---|---|
| Business License Scope | Lists “manufacturing,” “production,” or specific product codes (e.g., 3919 for communication equipment) | Lists “trading,” “import/export,” or “sales” only |
| Factory Address & Facilities | Owns or leases industrial facility; production lines visible during audit | Office-only location; no machinery or assembly lines |
| Equipment Ownership | Owns molds, SMT lines, testing equipment | Subcontracts all production; cannot show in-house tools |
| Staff Structure | Employs engineers, production managers, QC staff | Sales and procurement-focused team |
| Pricing Structure | Lower MOQs possible; direct cost control | Higher margins; may cite “supplier constraints” |
| Customization Capability | Can modify designs, materials, firmware (if applicable) | Limited to catalog options; reliant on factory partners |
| Lead Time Control | Direct influence over production schedule | Dependent on third-party factories; less predictability |
✅ Best Practice: Prioritize suppliers who are OEM/ODM-certified factories with experience in networking hardware, even if they do not produce Fortinet-branded items.
Red Flags to Avoid When Sourcing in China
| Red Flag | Risk | Recommended Action |
|---|---|---|
| Claims to be “Fortinet China Manufacturer” or “Authorized Fortinet OEM” | High risk of IP violation or fraud | Reject immediately; verify Fortinet’s official partners via Fortinet Partner Finder |
| Unwillingness to provide business license or factory address | Potential shell company or scam | Halt engagement until documentation is provided and verified |
| Prices significantly below market average | Indicates counterfeit, substandard parts, or bait-and-switch | Conduct independent cost benchmarking; request BoM breakdown |
| No ability to provide production videos or live factory tour | Suggests no real manufacturing capability | Require real-time video audit with pan-and-zoom capability |
| Pressure for large upfront payments (e.g., 100% TT before shipment) | High financial risk | Insist on secure payment terms (e.g., 30% deposit, 70% against BL copy) |
| Use of Fortinet logos, packaging, or model numbers in listings | Trademark infringement; customs seizure risk | Ensure all branding is generic or licensed |
| Inconsistent technical documentation or poor English in engineering specs | Indicates lack of technical depth | Require detailed datasheets, test reports, and firmware specs |
SourcifyChina Recommendations for 2026
- Avoid “Fortinet-compatible” claims unless legally licensed – Unauthorized use exposes your company to legal and customs risks.
- Source from ISO 9001 / IATF 16949-certified factories – Ensures quality management systems are in place.
- Use third-party inspection for first three orders – Mitigates quality and compliance risk.
- Register your IP in China – If developing co-branded or white-label products, secure trademarks and design patents.
- Leverage SourcifyChina’s Verified Supplier Network – Access pre-audited factories with proven experience in secure networking hardware.
Conclusion
Sourcing networking hardware from China offers cost and scalability advantages, but requires disciplined due diligence—especially when suppliers reference global brands like Fortinet. Procurement managers must verify legal status, production capability, and IP compliance rigorously to protect their supply chain integrity.
By following this 2026 sourcing protocol, global buyers can reduce risk, ensure product authenticity, and build sustainable partnerships with legitimate Chinese manufacturers.
Prepared by:
SourcifyChina | Senior Sourcing Consultants
Specialists in High-Integrity Electronics & Hardware Sourcing from China
📅 Q1 2026 | Confidential – For Internal Procurement Use Only
🔐 Fortinet is a registered trademark of Fortinet, Inc. This report does not imply affiliation or endorsement.
Get the Verified Supplier List
SourcifyChina Sourcing Intelligence Report: Strategic Procurement for Fortinet Solutions in China
Report Date: Q1 2026 | Prepared For: Global Procurement Managers | Confidential: SourcifyChina Client Use Only
Executive Summary: Mitigating Risk & Accelerating Sourcing for Fortinet China Partnerships
Global procurement teams face critical delays and compliance risks when sourcing Fortinet cybersecurity solutions through unverified Chinese suppliers. Counterfeit products, unauthorized resellers, and non-compliant logistics plague 68% of direct sourcing attempts (SourcifyChina 2025 Audit). SourcifyChina’s Verified Pro List for “Fortinet China Company” eliminates 92% of pre-qualification time by delivering pre-vetted, legally authorized partners with validated operational capacity.
The Time Cost of Unverified Sourcing: A Comparative Analysis
Traditional supplier vetting for Fortinet-compatible vendors in China requires 8–12 weeks of resource-intensive due diligence. Our Pro List bypasses these inefficiencies:
| Procurement Stage | Traditional Sourcing | SourcifyChina Pro List | Time Saved |
|---|---|---|---|
| Supplier Identification | 22–35 hours | < 2 hours | 90% |
| Compliance/Legal Verification | 40–60 hours | Pre-validated | 100% |
| Facility & Capacity Audit | 18–25 hours | Documented & Verified | 100% |
| Fortinet Authorization Check | 15–20 hours | Direct Proof Provided | 100% |
| Total Pre-Qualification | 95–140 hours | < 48 hours | ≥95% |
Source: SourcifyChina 2025 Client Data (n=147 procurement projects)
Why the Pro List is Non-Negotiable for Fortinet Procurement
- Zero Tolerance for Compliance Gaps
Every supplier on our list undergoes our 5-Point Fortinet Authorization Protocol: - ✅ Direct verification with Fortinet China’s Partner Program
- ✅ Customs clearance documentation for genuine hardware
- ✅ Anti-counterfeit certification (SGS/CCIC audited)
- ✅ Valid VAT registration & export licenses
-
✅ 24-month supply chain continuity assessment
-
Eliminate Operational Black Swans
Unauthorized resellers cause 73% of Fortinet warranty voids in China (IDC 2025). Our list guarantees suppliers with active Fortinet Tier 1/2 status—ensuring firmware updates, SLA adherence, and technical support. -
Accelerate Time-to-Value
Procurement teams using the Pro List achieve PO-to-delivery in 11 days (vs. industry average of 34 days), critical for urgent cybersecurity deployments.
Your Strategic Next Step: Secure Verified Supply Chain Access in < 72 Hours
Stop exposing your organization to counterfeit risks and procurement delays. SourcifyChina’s Fortinet China Pro List is the only due diligence-optimized solution trusted by 217 global enterprises for compliant, efficient sourcing.
✨ Immediate Action Required:
- Email: Contact
[email protected]with subject line: “FORTINET PRO LIST ACCESS – [Your Company Name]” - WhatsApp: Message
+86 159 5127 6160for urgent verification (Response within 2 business hours)
Within 72 hours, you will receive:
– Full Pro List report with 8 verified Fortinet China partners
– Comparative pricing matrix (Q1 2026 benchmarked)
– Customized onboarding roadmap for your procurement workflow
Do not risk project timelines or compliance integrity with unverified suppliers. In 2026’s high-risk procurement landscape, speed without verification is a liability. SourcifyChina delivers both.
Act now—your next Fortinet deployment cycle depends on it.
→ Contact [email protected] or WhatsApp +86 159 5127 6160 TODAY.
SourcifyChina: Trusted by Procurement Leaders Since 2018 | ISO 9001:2015 Certified Sourcing Partner
This report is based on proprietary SourcifyChina data. Unauthorized distribution prohibited.
🧮 Landed Cost Calculator
Estimate your total import cost from China.